How Claude Code Enterprise Controls Changed Between August and October 2026: A Version-by-Version Analysis of Hooks, MCP Allow-Lists, and Gateway Policies
Across versions 2.1.251 to 2.1.316, Claude Code stripped permission bypasses from local repository files, introduced fail-closed hook primitives, and shifted policy enforcement to enterprise gateways.
Published: November 1, 2026 | Read time: ~10 min | Watch Video (Japanese)
Executive Summary: Enterprise Governance Across Ten Versions
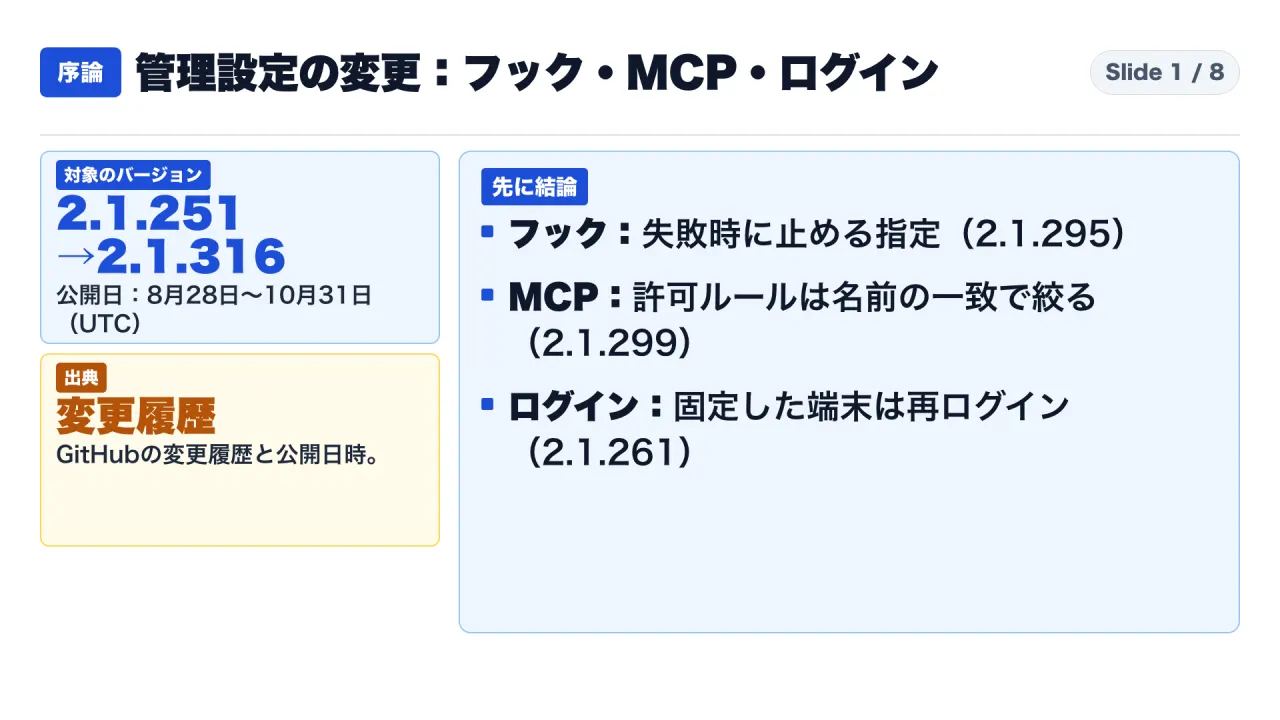
Between August 28, 2026, and October 31, 2026 (Universal Coordinated Time), Anthropic shipped ten updates to Claude Code, spanning version 2.1.251 through version 2.1.316. While user-facing announcements emphasized developer workflows, the official changelog reveals an architectural pivot in administrative governance.
Three operational areas underwent structural changes during this 64-day span:
- Execution Hooks: Added lifecycle events (
PreModelSwitch,PostModelSwitch), exact model version pinning (availableModelsMatch: "exact"), and fail-closed termination (onFailure: "block"). - Model Context Protocol (MCP) Governance: Reconfigured allow-lists (
allowedMcpServers), centralized distribution (managedMcpServers), and normalized exact-match scoping (mcp__<server>__*). - Authentication and Gateway Routing: Forced gateway authentication (
forceLoginMethod: "gateway"), hierarchical policy stacking (managed.policy_mode: layered), shared monthly group allocations (pooled_budget), and silent background application of server-managed configurations for Team and Enterprise tiers.
This briefing is prepared for infrastructure architects, corporate security officers, and systems administrators deploying coding agents. It examines what changed across releases and identifies operational risks if legacy configurations persist.
Methodology and Documented Boundaries
This review distinguishes statements into three evidentiary categories:
- Changelog Record: Information explicitly documented in Anthropic’s public repository changelog (
anthropics/claude-code/CHANGELOG.md), GitHub release manifests, or the Claude Platform documentation release notes. - Author Calculation: Deterministic calculations (such as timezone offsets between UTC and Japan Standard Time) computed from published timestamps.
- Interpretive Analysis: Comparative engineering evaluations, migration paths, and architectural deductions.
Four explicit boundaries govern this technical brief:
- Timestamp Normalization: All dates follow Universal Coordinated Time (UTC) from the GitHub releases API. Late afternoon UTC releases align with the subsequent calendar day in East Asian timezones (JST/KST).
- Exclusion of Undocumented Behaviors: Statements rely strictly on published notes without speculating on unstated vendor motivations.
- No Empirical Black-Box Verification: The behaviors reflect published specifications rather than local workstation experimentation.
- Targeted Administrative Scope: Analysis focuses strictly on permission boundaries, MCP server controls, hook lifecycles, and gateway authentication.
Section 1: Permission Scopes and Default Execution Modes
The balance between repository configuration files, user profiles, and central policies shifted toward defensive defaults.
Invalidation of Repository-Level Permission Bypasses
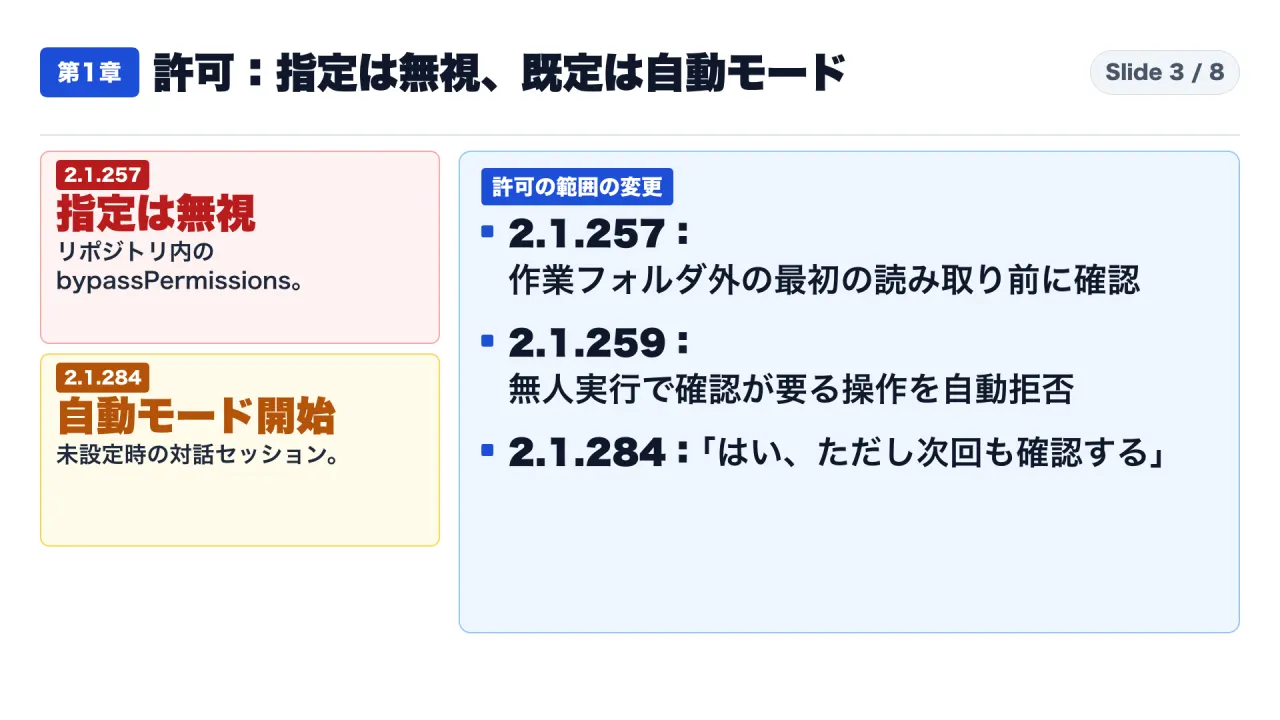
On September 1, 2026, version 2.1.257 altered the authority of project-level configuration files:
- Directives in repository settings (
.claude/settings.jsonor.claude/settings.local.json) settingdefaultMode: "bypassPermissions"are silently ignored and treated as auto mode. - Teams requiring unattended execution must set permissions in user settings, enterprise managed configurations, or pass explicit CLI arguments at startup.
Version 2.1.257 also introduced boundaries for automated execution. In auto mode, Claude Code prompts users before reading files outside the active working directory. To prevent traversal entirely, administrators can set permissions.blockReadsOutsideWorkingDirectories: true.
Headless Execution and Interactive Session Defaults
On September 2, 2026, version 2.1.259 introduced --permission-prompts none for automated execution pipelines. Operations requiring confirmation are automatically rejected while auto mode continues evaluating non-prompted actions.
On September 28, 2026, version 2.1.284 expanded directory boundaries:
- Added a “Yes, but ask again next time” option to the outside-directory read prompt.
- Interactive terminal and Visual Studio Code sessions without explicit permission configurations default to auto mode across all plans, though explicit
permissions.defaultModesettings retain precedence.
| Version | Date (UTC) | Behavioral Change | Directive |
|---|---|---|---|
| 2.1.257 | September 1, 2026 | Ignores repository defaultMode: "bypassPermissions" |
defaultMode |
| 2.1.257 | September 1, 2026 | Prompts before external directory read; adds block flag | permissions.blockReadsOutsideWorkingDirectories |
| 2.1.259 | September 2, 2026 | Rejects prompt-requiring actions in headless mode | --permission-prompts none |
| 2.1.284 | September 28, 2026 | Adds single-turn approval to external directory prompts | Interactive prompt |
| 2.1.284 | September 28, 2026 | Unconfigured interactive sessions default to auto mode | permissions.defaultMode |
Section 2: MCP Server Governance and Allow-List Mechanics
Model Context Protocol (MCP) integrations require balancing external connectivity with endpoint governance.
Centralized MCP Distribution and Allow-List Scoping
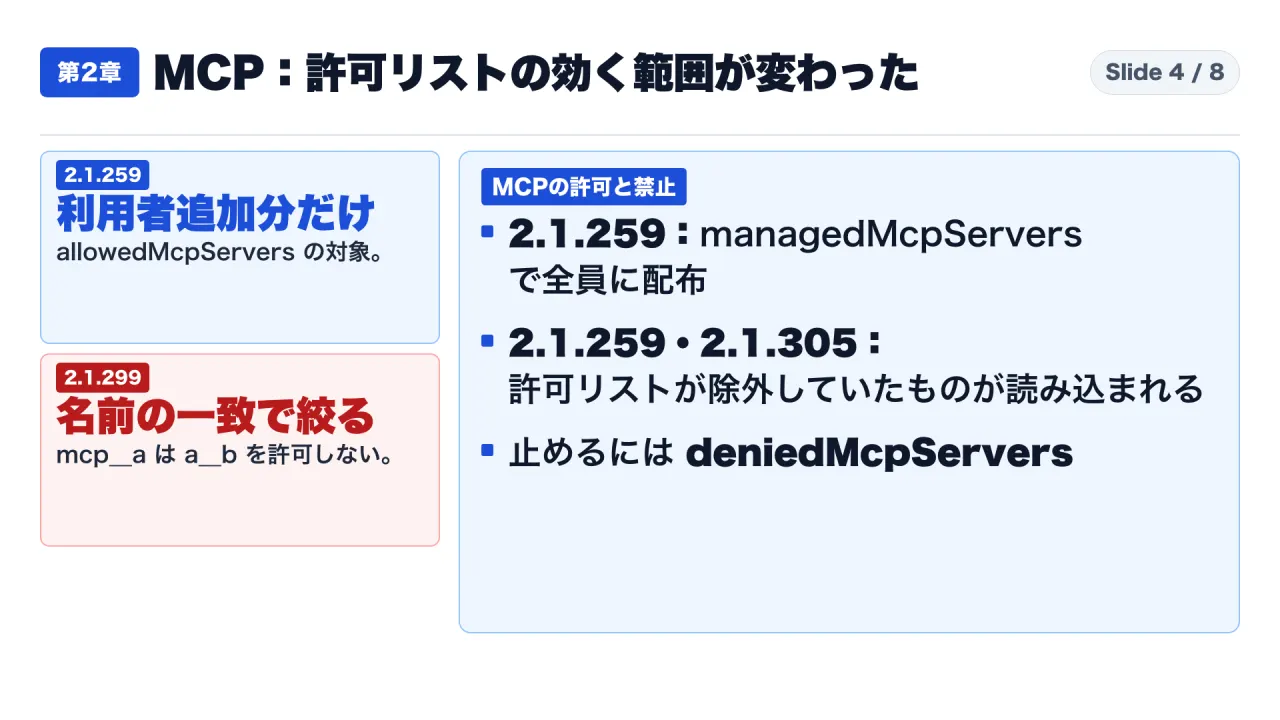
On September 2, 2026, version 2.1.259 introduced managedMcpServers. Administrators can provision uniform HTTP and Server-Sent Events (SSE) MCP endpoints across an organization using .mcp.json schemas. Command-line (stdio) tools in managed configurations are skipped.
Version 2.1.259 modified allowedMcpServers in a critical manner:
allowedMcpServersfilters only user-configured servers.- Centrally distributed servers in
managed-mcp.jsonpreviously suppressed by an allow-list load automatically upon upgrading to 2.1.259. - Restricting managed servers now requires explicit placement in
deniedMcpServers.
Exact-Match Scoping and Environment Variable Rules
On October 14, 2026, version 2.1.299 addressed prefix collisions in tool permission rules. A rule defining mcp__a no longer matches servers named a__b or a_. Rule definitions using mcp__<server>__* require the complete normalized server identifier.
On October 20, 2026, version 2.1.305 unblocked command-line stdio servers in managed-mcp.json where environment variable expansion (${VAR}) is restricted to env fields. These tools load automatically unless registered in deniedMcpServers.
| Version | Date (UTC) | Behavioral Change | Directive |
|---|---|---|---|
| 2.1.259 | September 2, 2026 | Adds central HTTP/SSE distribution; skips stdio tools | managedMcpServers |
| 2.1.259 | September 2, 2026 | allowedMcpServers scopes only user tools; unblocks managed tools |
allowedMcpServers, deniedMcpServers |
| 2.1.299 | October 14, 2026 | Enforces exact normalized server matching | mcp__<server>__* |
| 2.1.305 | October 20, 2026 | Unblocks managed stdio servers with env-restricted ${VAR} |
allowedMcpServers, deniedMcpServers |
Section 3: Hook Lifecycles, Fail-Closed Security, and Inference Hooks
Hooks allow organizations to insert programmatic gates into agent workflows.
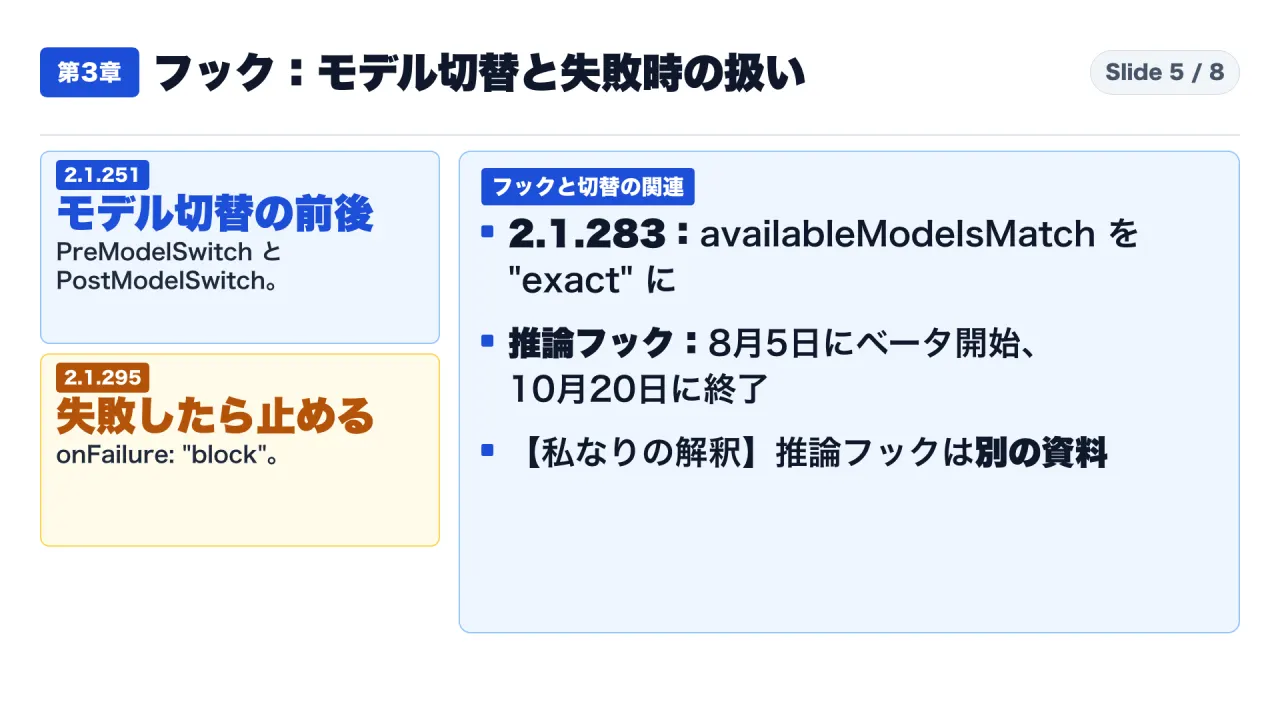
Model Interception and Catalog Locking
On August 28, 2026, version 2.1.251 added PreModelSwitch and PostModelSwitch hook events, allowing external scripts to block, confirm, or annotate transitions between models.
On September 25, 2026, version 2.1.283 added availableModelsMatch: "exact". This setting restricts accessible models to explicit versions listed in availableModels. Unlisted foundation model versions remain blocked until administrators update configuration catalogs.
Fail-Closed Execution: onFailure: "block"
On October 8, 2026, version 2.1.295 introduced onFailure: "block" for command and HTTP hooks. If a hook script fails to launch, exceeds timeouts, or returns non-zero exit codes, the operation is blocked. Omission of this flag causes hooks to fail open.
Enterprise Inference Hooks
Concurrently, Anthropic deployed centralized inference hooks on the Claude Platform. Enterprise prompts can be directed through corporate AI security gateways for cryptographic verification:
- Public beta began August 5, 2026, for Claude Enterprise.
- General availability concluded the beta on October 20, 2026.
- Every blocked transaction is audited in the compliance Activity Feed.
| Version / Source | Date (UTC) | Behavioral Change | Feature / Directive |
|---|---|---|---|
| 2.1.251 | August 28, 2026 | Intercepts model switching lifecycle | PreModelSwitch, PostModelSwitch |
| 2.1.283 | September 25, 2026 | Restricts catalog strictly to declared versions | availableModelsMatch: "exact" |
| 2.1.295 | October 8, 2026 | Enforces fail-closed blocking on hook failure | onFailure: "block" |
| Platform Release | August 5, 2026 | Beta launch for AI security gateway inference hooks | Enterprise Inference Hooks |
| Platform Release | October 20, 2026 | General availability for enterprise inference hooks | Enterprise Inference Hooks |
Section 4: Enterprise Authentication and Gateway Routing
Authentication governance shifted from local workstation credentials to centralized gateways.
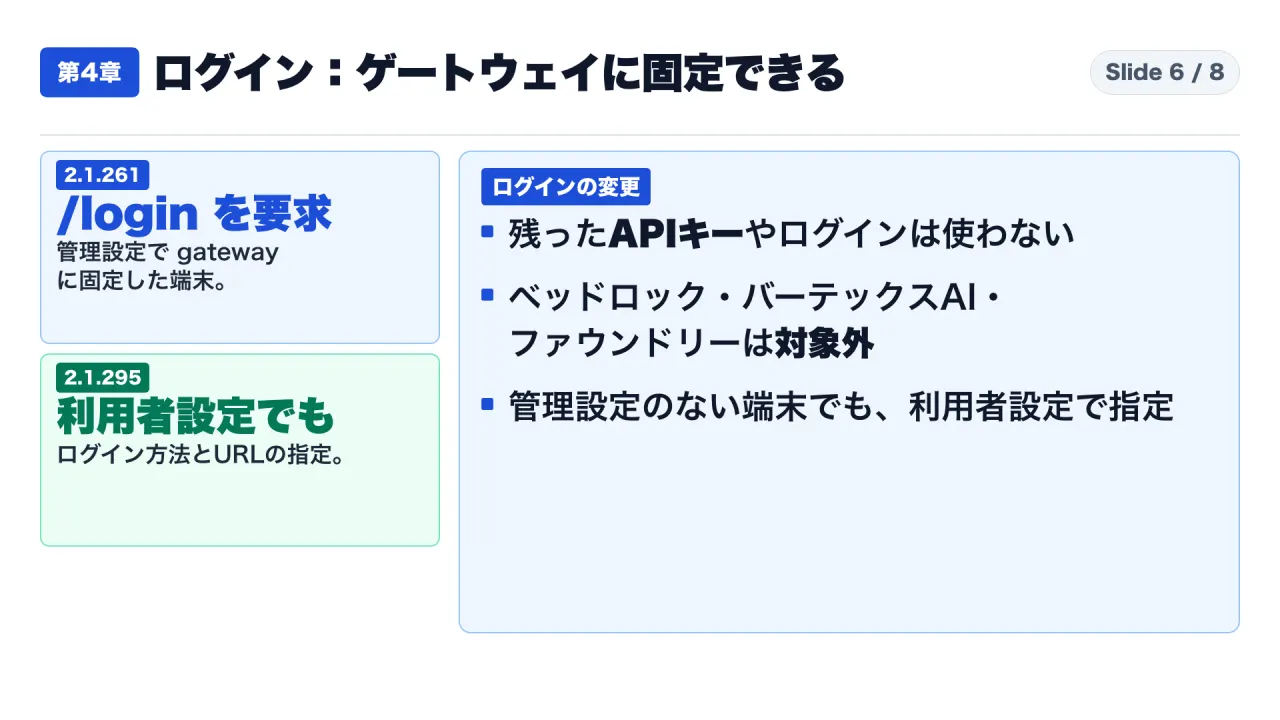
Gateway Enforcement on Managed and Unmanaged Endpoints
On September 4, 2026, version 2.1.261 modified authentication for managed machines. Setting forceLoginMethod: "gateway" mandates interactive terminal /login flows against the enterprise gateway, overriding stored local API keys or claude.ai browser sessions. Cloud provider environments (Amazon Bedrock, Google Cloud Vertex AI, and Microsoft Foundry) are excluded.
On October 8, 2026, version 2.1.295 allowed unmanaged machines to specify forceLoginMethod: "gateway" and forceLoginGatewayUrl in local user profiles, routing authentication to the corporate gateway.
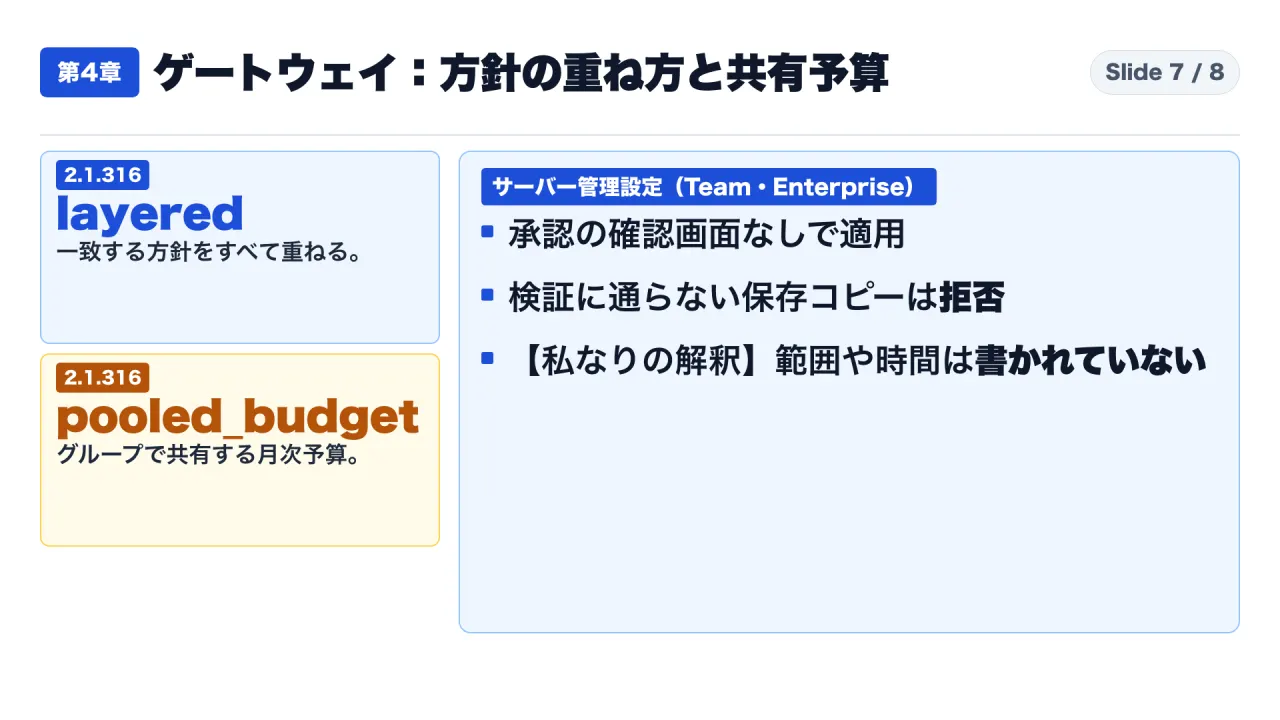
Hierarchical Policies, Group Budgets, and Automated Rollout
On October 31, 2026, version 2.1.316 introduced three administrative capabilities:
- Layered Policy Mode: Setting
managed.policy_mode: layeredrecursively merges all applicable organizational policies top-to-bottom. - Pooled Budgets: Added shared monthly group spending allocations via
pooled_budgetin the spending limits management API. - Automated Settings Delivery: Server-managed configurations for Team and Enterprise tiers apply automatically without interactive developer approval prompts. Cached files failing cryptographic checks are rejected.
| Version | Date (UTC) | Behavioral Change | Directive |
|---|---|---|---|
| 2.1.261 | September 4, 2026 | Forces gateway login; ignores local keys (Bedrock/Vertex/Foundry excluded) | forceLoginMethod: "gateway" |
| 2.1.295 | October 8, 2026 | Enables gateway enforcement in user profiles | forceLoginMethod, forceLoginGatewayUrl |
| 2.1.316 | October 31, 2026 | Evaluates matching gateway policies hierarchically | managed.policy_mode: layered |
| 2.1.316 | October 31, 2026 | Implements pooled monthly team budget allocations | pooled_budget |
| 2.1.316 | October 31, 2026 | Applies verified server configurations without prompts | Team/Enterprise Engine |
Structural Alignment: Configuration Tier Precedence
Administrative precedence in Claude Code operates across distinct levels:
- Repository Settings (
.claude/settings.json): Bypasses stripped; version 2.1.257 ignoresbypassPermissions. - User Settings (
~/.claude/settings.json): Preserves preferences and supports unmanaged gateway configuration (2.1.295). - Managed System Settings (
/etc/claude/): Distributes MCP servers (2.1.259), locks models (2.1.283), and forces gateway authentication (2.1.261). - Server Policies (Gateway): Merges layered policies, tracks pooled budgets, and updates clients silently (2.1.316).
Chronological Release Ledger
The table below lists release timings in Universal Coordinated Time (UTC) and Japan Standard Time (JST).
| Version | Date & Time (UTC) | Date & Time (JST) | Calendar Delta |
|---|---|---|---|
| 2.1.251 | August 28, 2026 at 18:19 | August 29, 2026 at 03:19 | +1 Day |
| 2.1.257 | September 1, 2026 at 17:53 | September 2, 2026 at 02:53 | +1 Day |
| 2.1.259 | September 2, 2026 at 22:33 | September 3, 2026 at 07:33 | +1 Day |
| 2.1.261 | September 4, 2026 at 19:58 | September 5, 2026 at 04:58 | +1 Day |
| 2.1.283 | September 25, 2026 at 21:50 | September 26, 2026 at 06:50 | +1 Day |
| 2.1.284 | September 28, 2026 at 18:02 | September 29, 2026 at 03:02 | +1 Day |
| 2.1.295 | October 8, 2026 at 19:48 | October 9, 2026 at 04:48 | +1 Day |
| 2.1.299 | October 14, 2026 at 02:49 | October 14, 2026 at 11:49 | Same Day |
| 2.1.305 | October 20, 2026 at 20:46 | October 21, 2026 at 05:46 | +1 Day |
| 2.1.316 | October 31, 2026 at 01:01 | October 31, 2026 at 10:01 | Same Day |
Eight of the ten releases occurred during North American hours, corresponding to the subsequent morning in Tokyo.
Administrative Audit Checklist: Six Mandatory Review Items
Security and IT administrators managing Claude Code deployments should audit their infrastructure against the following six criteria:
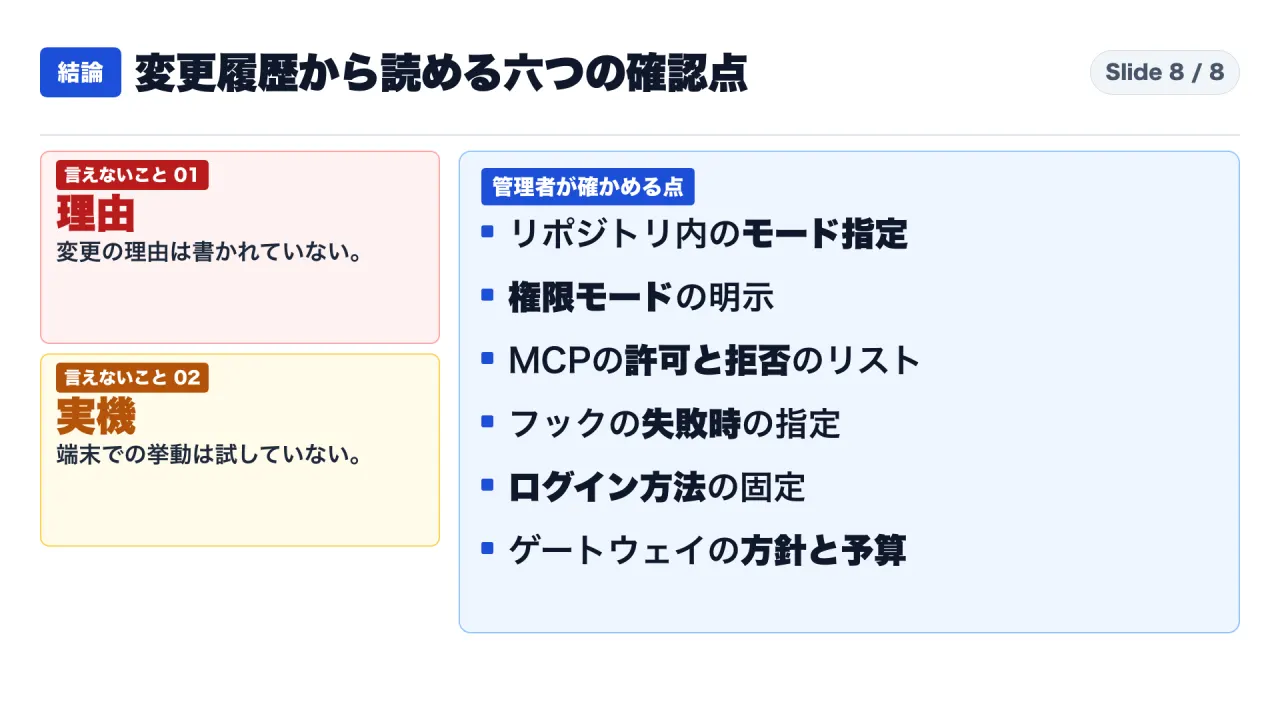
- Remove Repository Bypasses: Audit internal repositories for
.claude/settings.jsonspecifyingdefaultMode: "bypassPermissions". This directive has been non-functional since version 2.1.257. - Explicitly Set Interactive Defaults: In version 2.1.284 and above, unconfigured interactive sessions enter auto mode. Organizations requiring manual confirmations must configure
permissions.defaultMode. - Transition to MCP Deny-Lists: Because versions 2.1.259 and 2.1.305 unblocked
managed-mcp.jsontools fromallowedMcpServers, administrators who relied on allow-lists to block default tools must migrate restricted servers intodeniedMcpServers. Verify all patterns use full normalized names following the 2.1.299 standard. - Enforce Fail-Closed Hook Directives: Review custom pre- and post-execution hook declarations. Configure
onFailure: "block"(available since version 2.1.295) to prevent operations from silently proceeding when security tools encounter errors. - Verify Gateway Routing Placement: Determine whether workstations enforce gateway routing via central managed configurations (
forceLoginMethod: "gateway") or user-level configuration files. - Audit Gateway Layering and Shared Budgets: Teams utilizing version 2.1.316 should review whether
managed.policy_mode: layeredis active and verify how cascading policy documents resolve precedence across organizational units. Validate that shared team consumption aligns withpooled_budgetallocations.
Primary Sources and References
- Anthropic, Claude Code Public Repository CHANGELOG: https://raw.githubusercontent.com/anthropics/claude-code/main/CHANGELOG.md
- Anthropic, Claude Code GitHub Releases API Manifest: https://api.github.com/repos/anthropics/claude-code/releases
- Anthropic, Claude Platform Technical Release Notes: https://platform.claude.com/docs/en/release-notes/overview